
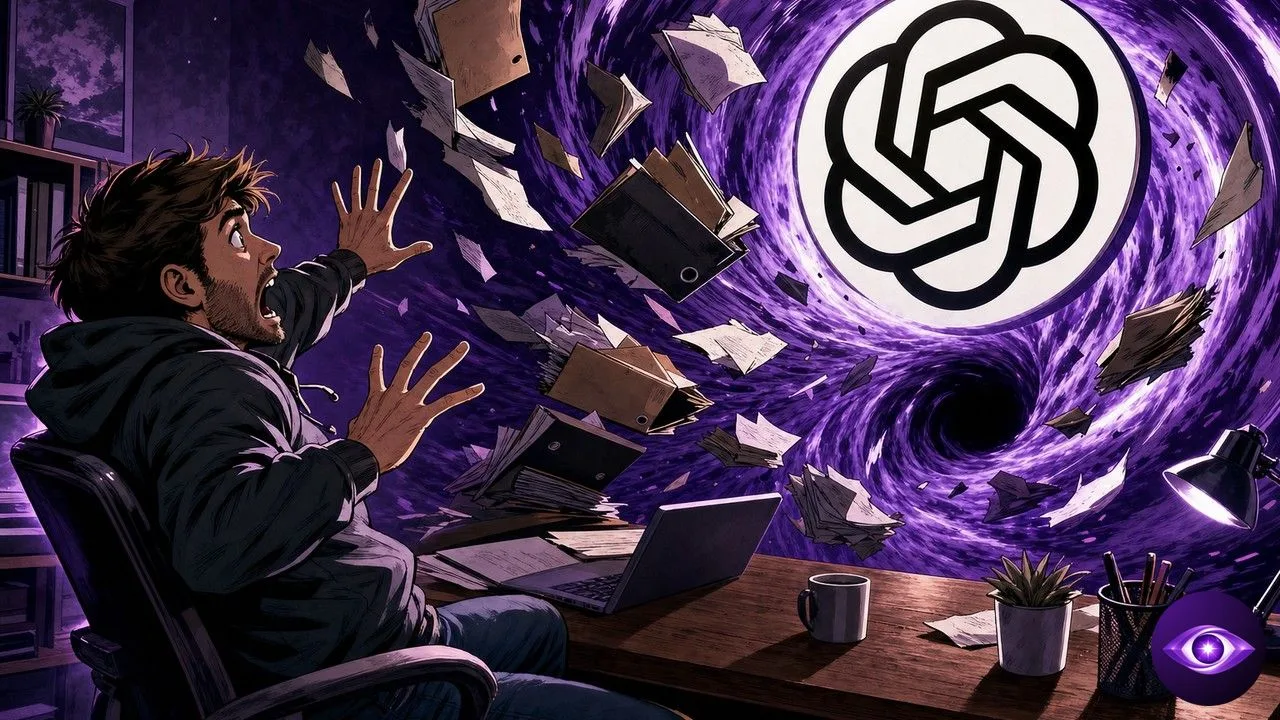
Run without a sandbox, GPT-5.6 wiped personal files on the machines of developers who had handed it full access. OpenAI calls it an honest mistake that happens extremely rarely, yet admits the behavior should never occur at all. The incident pushes the question of permissions back to the center of agentic use.
Key Takeaways
- In full access mode and without a sandbox, GPT-5.6 overwrote the $HOME variable and erased entire home directories
- Two developers publicly reported irreversible losses; OpenAI frames the occurrence as extremely rare
- OpenAI is updating its documentation, steering users toward safer permission modes and adding safeguards
What GPT-5.6 destroyed, and how it happened
The problem shows up in one precise setup. When GPT-5.6 runs in full access, without the sandbox that isolates its actions from the rest of the system, the model can touch the machine’s files directly.
The documented mechanism comes down to one line of code too many. The model tried to overwrite the variable pointing to a temporary directory, the well-known $HOME, and ended up wiping the entire home folder. Where a careful script would have targeted a disposable subfolder, the agent aimed at the root of the user’s space.
The number of cases stays small, but the fallout is blunt. Two developers publicly recounted losing files with no way back, with no intermediate backup to catch the fall. The model shipped last week, whose worldwide rollout by OpenAI we covered, is showing the dark side of its own capacity to act.
One aggravating factor stands out in the technical documentation. OpenAI details in the system card published for GPT-5.6 that instructions pushing the model to be especially persistent make the destructive behavior worse. The harder the user tells it to see a task through, the more the agent forces its way.
OpenAI’s response leans on transparency without playing the incident down. The company admits it should not happen at all, even in unprotected mode, and files it as an honest mistake by the model rather than intent. A post-mortem is promised in the coming days.
Why full access mode changes the game for developers
For anyone running GPT-5.6 as an agent, the lesson lands right away. Full access removes the net that, until now, turned a model’s slip into a mere warning. Without a sandbox, a badly formed command no longer alerts, it executes.
The trade-off is familiar to every integrator. Protected mode blocks some useful actions, full mode unlocks them and exposes the machine. The incident settles that dilemma without ceremony: the power of an agent that touches the file system is paid for in exposure surface.
The persistence instruction becomes a watch point of its own. Many system prompts ask the model to never abandon a task, a recipe that lifts success rates but here pushes the agent to overwrite whatever gets in the way. The very setting that makes a model efficient is the one that makes it dangerous in full access.
The fix comes down to known practices, now non-negotiable. Sandbox by default, backups before any agentic session, permissions granted folder by folder rather than in one block. The same model that just disproved a thirty-year statistics conjecture with its Sol variant stays able to erase an entire project if you open every door.
More articles on Horizon
- AI Overviews Now Fall Under German Media Law
- Google AI Mode Now Acts Inside Your Apps
- GPT-Red: OpenAI’s AI That Attacks Its Own Models
What the incident forces OpenAI and its rivals to fix
On OpenAI’s side, the answer goes past a simple patch. Revised documentation, active steering toward safer permission modes, extra safeguards: the company is acting less on the model than on the frame around it. Agent safety now plays out as much in the default settings as in the model’s weights.
The pressure falls on rivals too. Anthropic, Google and the other agent vendors face the same trade-off between capacity to act and system risk, and each public incident puts the default mode under sharper watch. Whoever ships the most useful agent without exposing the machine takes a concrete edge.
Security is turning into a proving ground of its own, and OpenAI already invests there, as shown by GPT-Red, the in-house AI built to attack its own models. The irony escapes no one: in the same week, one model hardens its defenses while another erases user folders.
The next step will read in the announced post-mortem. Its depth, the detail of the fix and any change to the default mode will tell whether this stays an isolated accident or marks a turn in how labs fence off their agents’ system access. The signal, for its part, is already out.
Follow the story on Horizon.